Back to Blog
Cybersecurity

The Klue Breach and the OAuth Tokens Everyone Forgot About

A single forgotten credential, about four years old, gave attackers a foothold that turned into a breach touching roughly 200 companies through nothing more exotic than stolen OAuth tokens. Here is how the Klue incident happened and what it means for any business running third-party integrations.

AetherGuard Team June 16, 2026 6 min read
The Klue Breach and the OAuth Tokens Everyone Forgot About

A Four-Year-Old Credential

On June 12, Klue, a competitive intelligence platform used by sales and marketing teams, discovered something was wrong inside its integration systems. When the investigation wrapped up, the root cause turned out to be almost mundane: a legacy service account credential, reportedly around four years old, that nobody had rotated or retired.

That is the whole story, really. Not a zero-day. Not an especially sophisticated exploit chain. A credential that should have been killed off years earlier, still sitting there, still valid, still connected to production systems.

What Happened After the Attacker Got In

Once inside, the attacker pushed a malicious code update into Klue's integration infrastructure, built to do one specific thing: harvest the OAuth tokens connecting Klue to its customers' other business tools. Salesforce was the primary target, but the same mechanism reached connections to Gong, HubSpot, and Slack as well.

With valid OAuth tokens in hand, the attacker did not need to break into anything else. They wrote automated scripts that called Salesforce's own REST API endpoints, the same ones Klue's legitimate integration used every day, and systematically pulled data out: business contacts, price quotes, internal sales communications, and account records. To Salesforce's systems, the requests looked exactly like what they were supposed to look like, because the tokens making them were real.

Roughly 200 companies were affected. Some of the confirmed names are notable for a reason that should sting a little: Huntress, Recorded Future, and Tanium, three cybersecurity companies, were on the list, alongside Jamf, Gong, Sprout Social, and Insurity. An extortion group calling itself Icarus claimed responsibility and began pressuring victims directly through emails and a leak site. Salesforce's response was to disable Klue's Battlecards app integration platform-wide, cutting off the attacker's access path for every remaining customer at once.

This Was Not an Isolated Incident

A few weeks earlier, a much larger campaign hit more than 700 organizations through a similar mechanism: stolen OAuth tokens tied to the Salesloft Drift integration with Salesforce. That attacker, tracked as UNC6395, spent roughly ten days in June pulling data out of connected Salesforce instances, with particular interest in support case text, where employees had pasted things like AWS keys, Snowflake tokens, VPN credentials, and plaintext passwords while troubleshooting issues.

Two separate incidents, two different vendors, the same underlying weakness: a third-party integration holding a long-lived OAuth token that, once stolen, works exactly as well for an attacker as it does for the app it was issued to.

Why OAuth Tokens Are the New Soft Target

Every time a business connects a third-party app to Salesforce, Google Workspace, Slack, or any other core platform, that app receives an OAuth token acting on the company's behalf, often with broad, standing permissions and no expiration date in sight. Most companies can name every employee with access to their CRM. Very few can produce a complete, current list of every app connected to it, what permissions each one holds, and when each token was last used.

That blind spot is exactly what attackers have learned to exploit. Rather than going after Salesforce directly, a well-defended target, they go after the smaller vendor with weaker security that happens to hold a key to the front door.

What Your Business Should Do

Start by inventorying every connected app across Salesforce, Google Workspace, Microsoft 365, and anything else holding sensitive data. If you cannot say what is connected and why, that is the first problem to fix. Kill what you do not use. Any integration nobody remembers setting up, or that was set up by someone who no longer works there, should be revoked outright. A dead integration with a live token is pure risk with no upside.

Rotate tokens and service account credentials on a schedule. A four-year-old credential should never still be active anywhere in your environment. Treat service accounts and app integrations the same way you treat employee passwords, with an expiration date and a rotation policy behind them.

Stop pasting secrets into support tickets and CRM fields. The Salesloft Drift campaign succeeded in part because employees had left API keys and credentials sitting in plain text inside support case notes. Anything typed into a ticket, a chat message, or a CRM note should be treated as something an attacker could eventually read.

Finally, monitor API activity for anomalies. Unusual query patterns, requests against endpoints your integration does not normally use, or a sudden spike in data volume pulled through an API are often the only warning you get before a breach like this becomes public.

The Takeaway

The Klue breach did not require a brilliant attacker. It required an ordinary oversight, left alone for four years, in a system most people never think to audit. That is the uncomfortable truth behind most supply chain breaches: the mechanism is usually simple, and the failure is usually something a routine audit would have caught.

AetherGuard Technologies helps businesses map their third-party integrations, audit OAuth permissions, and build the kind of ongoing credential hygiene that keeps a four-year-old mistake from becoming next year's headline.
More Articles

The Man Hired to Stop Ransomware Gangs Just Got Charged With Helping One
Threat Intelligence

The Man Hired to Stop Ransomware Gangs Just Got Charged With Helping One

Companies pay ransomware negotiators for one reason: to stand between them and the criminals holding their data hostage. On October 8, federal agents arrested one of the negotiation industry's own co founders and accused him of conspiring with the hackers he was supposed to be negotiating against. Here is what his arrest adds to the FBI's ShinyHunters investigation, and what it says about an entire industry built on trust nobody can actually verify.

October 9, 2026 6 min read
The Anti-Cheat Bot Built to Protect Discord Servers Just Leaked 28 Million Accounts
Data Privacy

The Anti-Cheat Bot Built to Protect Discord Servers Just Leaked 28 Million Accounts

You never installed it yourself. A server admin did, months or years ago, to keep out alt accounts and raid bots, and you clicked accept without thinking twice. On October 4, that decision came back to affect roughly 28 million Discord users when the security bot meant to protect their communities got breached instead. Here is what happened, and why the apps you never personally chose are often the ones holding the most data about you.

October 8, 2026 6 min read
The 'Cybersecurity Company' Seven Countries Just Accused of Spying for Beijing
Cybersecurity

The 'Cybersecurity Company' Seven Countries Just Accused of Spying for Beijing

A company with offices, a payroll, and a name that sounds like any other IT vendor spent years breaking into government networks across Southeast Asia on behalf of Chinese intelligence services. On October 8, the FBI and six partner nations named it publicly, and the technical details of how it operated are a useful lesson for any organization that still thinks of hacking as something done by lone individuals in hoodies rather than companies with HR departments.

October 7, 2026 7 min read
Inside the $351 Million Bitget Hack: How Attackers Stole Crypto Without Stealing a Key
Threat Intelligence

Inside the $351 Million Bitget Hack: How Attackers Stole Crypto Without Stealing a Key

Bitget lost 351.6 million dollars across seven blockchains after attackers manipulated the exchange's own backend into approving transfers it should have rejected. The exchange says its private keys were never touched, which is exactly what makes this one worth understanding.

September 26, 2026 6 min read
SalesBleed: How Three Flaws Turned Salesforce's AI Agent Against the Companies Using It
Cybersecurity

SalesBleed: How Three Flaws Turned Salesforce's AI Agent Against the Companies Using It

A single untrusted submission through an ordinary contact form could hijack a company's own trusted Salesforce AI agent, pull sensitive CRM data out the back door, and send phishing messages from inside its own Slack. Here is how SalesBleed worked and what it means for every business now plugging AI agents into public facing tools.

September 25, 2026 6 min read
When the FBI Gets Hacked: What the ShinyHunters Jobs Portal Breach Means for Everyone Else
Threat Intelligence

When the FBI Gets Hacked: What the ShinyHunters Jobs Portal Breach Means for Everyone Else

The extortion group ShinyHunters claims it stole sensitive data on almost every FBI agent and job applicant by exploiting a hole in Oracle's PeopleSoft platform. Whether or not every detail holds up, the incident is a clean lesson in how supply chain risk does not care how well resourced an organization is.

September 24, 2026 6 min read
Astrana Health Breach Shows How a Spoofed Phone Number Can Beat Your Security
Data Privacy

Astrana Health Breach Shows How a Spoofed Phone Number Can Beat Your Security

No exotic exploit, no zero day, just a phone call that looked like it came from inside the building. Astrana Health's newly disclosed breach is a reminder that the weakest link in most companies' defenses is still the phone call nobody trained employees to question.

September 23, 2026 5 min read
The GTA 6 CyberLeek Incident: What a Video Game Leak Teaches Every Business About Digital Exposure
Data Privacy

The GTA 6 CyberLeek Incident: What a Video Game Leak Teaches Every Business About Digital Exposure

An account calling itself CyberLeek spent weeks leaking Grand Theft Auto VI gameplay footage, and Rockstar's parent company responded by subpoenaing Microsoft and Discord for the personal data of everyone who ever joined three specific Discord servers. Most of them did nothing wrong.

September 22, 2026 8 min read
CVE-2026-83548: The Perfect-Score SonicWall Flaw Attackers Started Exploiting Within Days
Vulnerability Management

CVE-2026-83548: The Perfect-Score SonicWall Flaw Attackers Started Exploiting Within Days

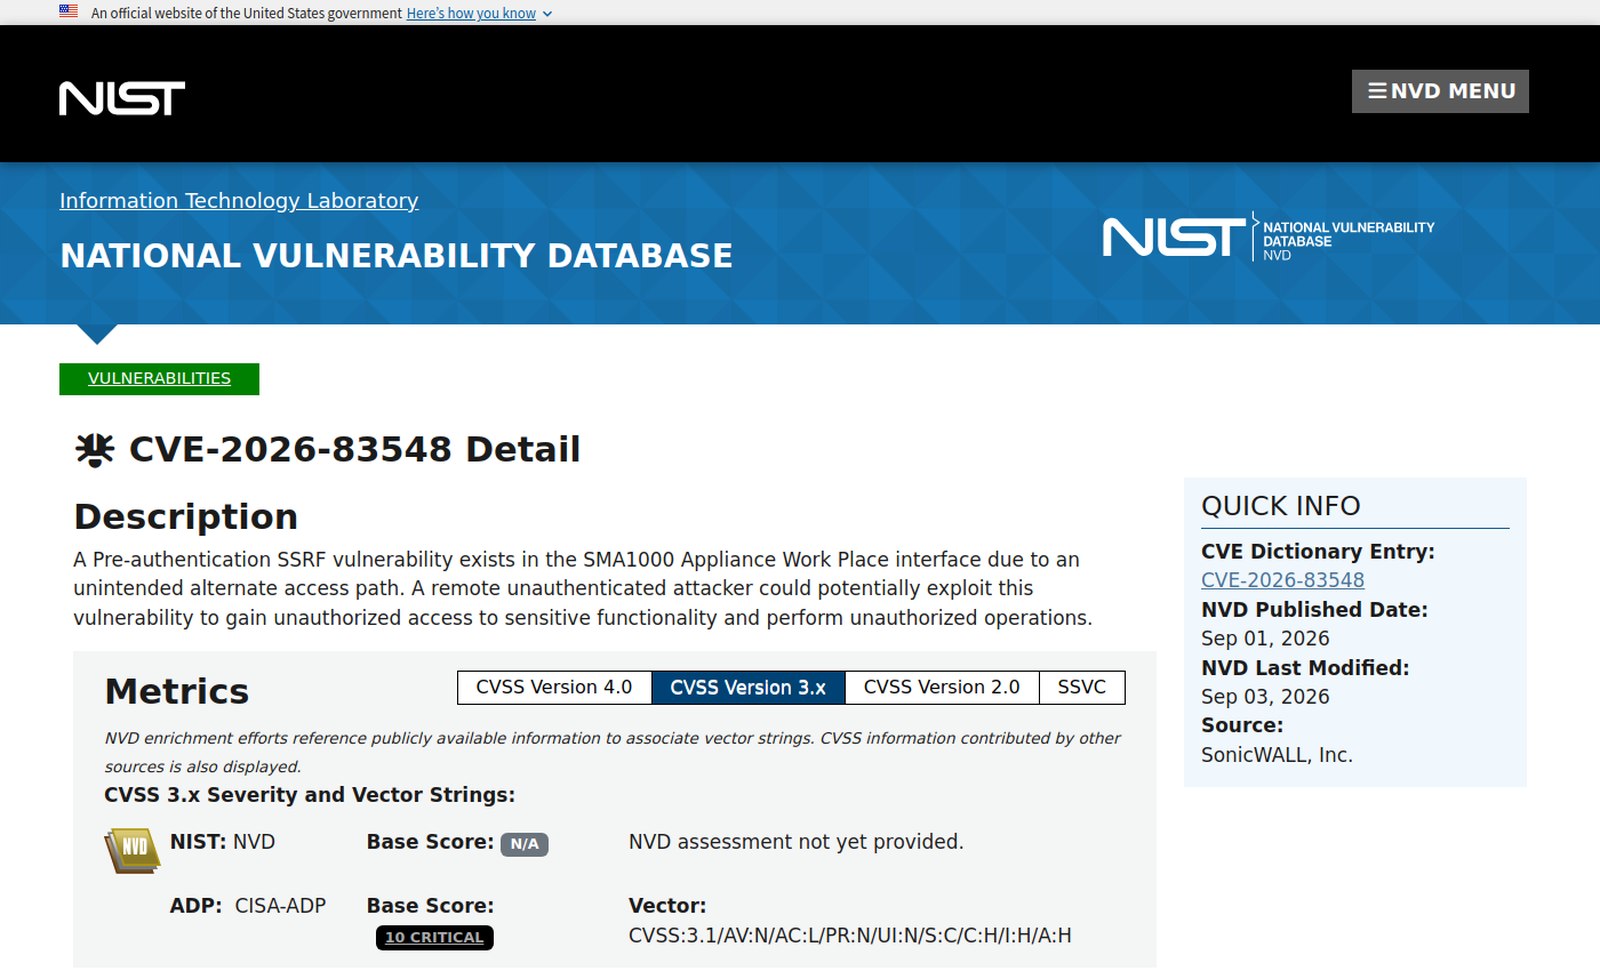
A pre-authentication SSRF vulnerability in SonicWall's SMA 1000 remote access appliances scored a full 10.0 on CVSS and was already under active attack by the time CISA added it to its Known Exploited Vulnerabilities catalog. Here is what it does and how to close it.

September 20, 2026 6 min read
The CenterPoint Energy Breach and the API Security Gap Almost Every Company Has
Data Privacy

The CenterPoint Energy Breach and the API Security Gap Almost Every Company Has

A Texas utility serving millions confirmed a breach of nearly seven million customer records after an attacker abused an unprotected public API. The mechanism was almost mundane, which is exactly why every organization running customer-facing APIs should be paying attention.

September 17, 2026 7 min read
Inside Boston Scientific's Cyberattack: When Recovery Takes Longer Than the Attack Itself
Cybersecurity

Inside Boston Scientific's Cyberattack: When Recovery Takes Longer Than the Attack Itself

A network outage at one of the world's largest medical device makers disrupted manufacturing and order shipping for weeks and forced the company to warn investors it may miss its full-year financial guidance. The real lesson here is about resilience, not just prevention.

September 10, 2026 6 min read
How a Flaw in an AI Gateway Became a Ransomware Group's Way In
Vulnerability Management

How a Flaw in an AI Gateway Became a Ransomware Group's Way In

LiteLLM is one of the most widely used tools for connecting company applications to AI models. A chained vulnerability in it reached a perfect CVSS score of 10.0, and the Qilin ransomware group has been linked to exploiting it. Here is what happened and what it says about the security of AI infrastructure broadly.

June 12, 2026 7 min read
The Stryker Attack: When a Cyberattack Is Retaliation, Not Extortion
Threat Intelligence

The Stryker Attack: When a Cyberattack Is Retaliation, Not Extortion

An Iran-linked group wiped more than 200,000 devices across medical device giant Stryker's global network and framed the attack as retaliation for a real-world military strike. Here is how it happened, why Stryker was targeted, and what it means for any company that looks like a symbolic target.

March 16, 2026 7 min read
Why Zero Trust Is the Future of Cybersecurity for Every Business
Cybersecurity

Why Zero Trust Is the Future of Cybersecurity for Every Business

The traditional perimeter-based security model is dead. Learn how the Zero Trust framework can protect your business from modern threats by verifying every user, device, and connection before granting access.

February 12, 2026 8 min read
5 Critical Steps for a Secure Cloud Migration
Cloud Solutions

5 Critical Steps for a Secure Cloud Migration

Moving to the cloud offers incredible benefits, but a poorly planned migration can expose your data to serious risks. Here are the five essential steps to ensure your cloud transition is secure and seamless.

January 28, 2026 6 min read
The Complete Guide to Preventing Ransomware Attacks
Threat Intelligence

The Complete Guide to Preventing Ransomware Attacks

Ransomware attacks on businesses increased 150% last year. This comprehensive guide covers the strategies, tools, and best practices you need to protect your organization from becoming the next victim.

January 15, 2026 10 min read
Data Breaches: How One Incident Can Affect Every Part of Your Life
Data Privacy

Data Breaches: How One Incident Can Affect Every Part of Your Life

A data breach is not just a headline. It is a life-altering event that can compromise your finances, identity, career, relationships, and mental health. Here is an in-depth look at the full impact and what you can do about it.

February 20, 2026 14 min read
The Foxconn Breach: When Ransomware Hits the Global Supply Chain
Threat Intelligence

The Foxconn Breach: When Ransomware Hits the Global Supply Chain

When the ransomware group Nitrogen hit Foxconn's North American factories, it did not just expose one company. It exposed schematics and project files tied to Apple, Nvidia, Dell, and more, showing how much risk sits inside a single supply chain link.

May 14, 2026 6 min read
Inside ShinyHunters: The Extortion Group Behind This Year's Biggest Breach Headlines
Data Privacy

Inside ShinyHunters: The Extortion Group Behind This Year's Biggest Breach Headlines

One extortion group has been linked to more than 40 breaches in 2026 alone, including an attack that disrupted school exams nationwide. Here is how ShinyHunters operates, why its methods keep working, and what to do if your data got caught in the blast radius.

May 8, 2026 7 min read
CVE-2026-50522: Inside the SharePoint Flaw That Went From Patch to Active Attack in Days
Vulnerability Management

CVE-2026-50522: Inside the SharePoint Flaw That Went From Patch to Active Attack in Days

A critical SharePoint vulnerability went from patch release to active exploitation in a matter of days, and the attackers are after more than just data. Here is what CVE-2026-50522 actually does and how to close the gap it leaves open even after you patch.

July 23, 2026 7 min read